How to Build Cyber Resilience Before the Next Crisis Hits
Key Highlights
- Prepare for plausible risks, not every possible crisis. Focus resilience planning on disruptions that are most likely to occur or would have the greatest impact on the business.
- Start with a risk assessment. Identify the most critical assets, assess how well they’re protected and prioritize investments accordingly.
- Test the plan before you need it. Tabletop exercises and realistic simulations can expose unclear responsibilities, decision-making gaps and other weaknesses before an actual disruption.
- Make resilience part of the culture. Cybersecurity and operational resilience aren’t solely IT responsibilities; leadership behavior and everyday employee decisions directly influence organizational risk.
- Treat resilience as continuous improvement. Businesses, technologies and threats constantly change. Resilience isn’t a one-time project; it requires ongoing assessment, testing and adjustment.
TL:DR
Organizations can’t predict every cyberattack, vendor failure, or operational disruption, but they can prepare to withstand them. Building resilience starts with understanding the risks that matter most, testing response plans under realistic conditions and creating a culture where preparedness is an ongoing business responsibility. The goal isn’t perfect protection … it’s ensuring the organization can respond, recover, and keep operating when disruption occurs.
Effective cyber resilience starts with understanding business risks, prioritizing investments and testing response plans before disruption puts them to the test.
The worst time to discover that a crisis plan doesn’t work is during the crisis. Yet organizations routinely enter periods of disruption with response plans that have never been tested, dependencies they don’t fully understand and risks they have evaluated more by instinct than evidence. Whether the threat is ransomware, financial fraud, a critical vendor outage or something leaders haven’t anticipated, resilience isn’t about accurately predicting what happens next. It’s about building an organization capable of responding when the prediction is wrong.
That distinction matters as businesses confront an environment in which disruption increasingly comes from multiple directions at once. Cyber threats evolve. Regulations change. Critical vendors experience outages. New technologies introduce new vulnerabilities.
Rather than attempting to prepare for every conceivable scenario, leaders can build cyber resilience by identifying critical assets, prioritizing the threats most likely to affect their operations and regularly testing their ability to respond and recover. For IT leaders, that means aligning cybersecurity investments and incident-response planning with the risks that matter most to the business.
Reg Harnish has spent more than two decades doing exactly that. The CEO of OrbitalFire Cybersecurity began working in cybersecurity around 2000 and later founded GreyCastle Security, where his team built cybersecurity programs for major organizations including Walmart, Toyota, Titleist and the NBA. Today, OrbitalFire focuses on translating the sophisticated cybersecurity and risk management practices used by large enterprises into approaches that work for smaller organizations, where resources are tighter, but the opportunity to meaningfully reduce risk can actually be greater.
How to prioritize the cyber risks that matter most
One reason organizations remain reactive is deceptively simple: It’s difficult to invest in something when you don’t understand its value.
For smaller organizations especially, spending on cybersecurity and resilience competes directly with other priorities. Leaders may understand the potential impact of a cyberattack but struggle to determine its likelihood or quantify what preventing one is worth.
Risk, Harnish explains, ultimately comes down to two questions: How likely is something to happen, and what will the impact be if it does?
Rather than preparing for the most frightening scenario in the headlines, organizations should concentrate on events most likely to affect their particular business or those capable of causing the greatest damage. For many companies, that means ransomware, financial fraud, business email compromise or disruption involving a critical third party.
That last category is becoming particularly important as organizations increasingly rely on cloud providers, software platforms, outsourced services and other partners. A cyberattack doesn’t need to strike your company directly to interrupt your operations. If a payroll provider, software platform or other critical vendor goes offline, its problem can quickly become yours.
That makes third-party dependencies an important consideration in both cybersecurity risk assessments and business continuity planning.
“Let’s practice something that’s meaningful,” Harnish says.
Why cyber resilience starts with a risk assessment
Before leaders can prepare for disruption, they need to understand what they are protecting.
That makes a risk assessment the foundation of a strong resilience strategy. Organizations cannot address every possible risk, and attempting to do so can waste resources that would be better directed elsewhere.
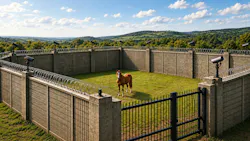
As Harnish puts it, “Don’t build a $100 fence around a $10 horse.”
A meaningful cybersecurity risk assessment starts by identifying the assets most valuable to the business, evaluating the threats that could compromise them and determining how well existing protections address those risks. That could include cash, customer data, intellectual property, trade secrets, critical systems or reputation. Leaders can then prioritize the investments most likely to reduce their organization's risk exposure.
The answers create a prioritized roadmap. One organization may need stronger authentication. Another may need better backups, employee training or improved recovery procedures.
The key is that the prescription should come from the organization’s actual risk profile, not from what a competitor is doing or what executives read in that morning’s headlines.
How tabletop exercises strengthen incident response
Having a plan is not the same as knowing it works.
Testing can range from simple exercises, such as asking employees to identify phishing emails, to technical assessments and full-scale incident-response simulations.
OrbitalFire, for example, conducts tabletop exercises — simulated incidents designed to test an organization's response plans and decision-making — built around fictional but "hyper-realistic" scenarios. Decision-makers receive an incident, defined responsibilities and a response plan, then must work through the evolving situation and make decisions under pressure.
That exercise can expose weaknesses a written plan never will.
During a ransomware incident, for example, executives may suddenly need to decide whether to involve law enforcement, bring in outside legal counsel or crisis communications support, communicate with customers and employees, address regulatory reporting requirements and support employees working extended hours to restore operations.
A realistic tabletop exercise helps organizations test those decisions in advance, revealing gaps in authority, communication and recovery responsibilities before an actual incident occurs.
The objective, Harnish says, is twofold: Restore normal business operations as quickly as possible and minimize the incident’s "blast radius."
The time to discover who has authority to make those decisions is not while systems are offline.
How leadership and employees shape cyber resilience
Technology alone cannot make an organization resilient.
Cybersecurity helps reduce the likelihood and impact of attacks, while cyber resilience also depends on the organization's ability to withstand disruption and recover when defenses fail. That requires more than technical controls.
“Every cybersecurity risk comes down to a human being and their behavior,” Harnish says.
That human could be an employee clicking a malicious link, a developer writing insecure code or an administrator improperly configuring a firewall. Conversely, employees who consistently make good security decisions can dramatically reduce organizational risk.
That makes culture a critical resilience tool.
Leadership sets that culture through how executives talk about cyber risk, the behaviors they reward and the expectations they establish. Cybersecurity can become part of job responsibilities, performance discussions, employee training and company-wide conversations rather than an issue delegated exclusively to IT.
Preparedness also requires repetition. Organizations that routinely practice responding to disruption are likely to react differently from those encountering a crisis playbook for the first time.
How to evaluate the business value of cyber resilience
Resilience also comes with trade-offs.
Security controls can create friction. Multi-factor authentication adds another step to logging into a system. Redundant systems cost money. Training takes employees away from other work.
But leaders should compare those costs with the potential cost of doing nothing.
How much employee time does an additional authentication step consume over a year? Now compare that with the downtime, lost productivity and financial consequences of ransomware, a compromised account or a manufacturing facility going offline.
There isn’t always one correct answer. The goal is to understand the economics well enough to make an informed decision.
That also means moving beyond viewing cybersecurity purely as a cost center. In some industries, stronger cybersecurity can become a competitive differentiator. A manufacturer capable of demonstrating stronger security practices than an otherwise comparable competitor may have an advantage when competing for sensitive work.
Cybersecurity, Harnish argues, can protect reputation, strengthen customer confidence, improve operations, and even support the sales process.
Why cyber resilience requires continuous improvement
Perhaps the most useful way to think about resilience is less like an IT project and more like personal fitness.
One trip to the gym doesn’t make someone healthy. Likewise, conducting one risk assessment or tabletop exercise doesn’t make an organization resilient.
Businesses change constantly. They hire employees, adopt applications, change vendors, enter new markets and acquire companies. Threats evolve alongside them. Cyber resilience strategies must therefore evolve as well, with periodic risk assessments and incident-response testing to account for changes in the business and its technology environment.
“Every business is on a different journey,” Harnish says. “They’re starting out in a different place, they’re moving in a different direction, they’re moving at a different speed. And that’s OK.”
The objective isn’t perfect protection. It’s continuous improvement: Understand what matters, identify meaningful risks, prepare for them, test the response and adjust as the business changes.
Smaller organizations shouldn’t assume their limited size puts resilience out of reach. Harnish argues that with fewer systems, people and layers of complexity, smaller companies can sometimes make meaningful improvements faster than massive enterprises.
The next disruption may be impossible to predict. The organization’s ability to withstand it doesn’t have to be.
About the Author
 Jess Mand
Contributor
Jess Mand is an award-winning communications strategist and founder of INDEMAND Communications, where she helps organizations translate complex ideas into clear, compelling narratives that drive connection and action. She partners with Fortune 500 companies, growth-stage firms, and mission-driven organizations to design communication strategies, content programs, and experiential campaigns that engage employees and elevate leadership messages. Known for her creative storytelling and pragmatic approach, Jess brings a rare blend of strategic insight and human-centered perspective to every project she leads.
 Resources
Quiz
Your Competitive Edge, DeliveredStay ahead of the curve with weekly insights into emerging technologies, cybersecurity, and digital transformation. TechEDGE brings you expert perspectives, real-world applications, and the innovations driving tomorrow’s breakthroughs, so you’re always equipped to lead the next wave of change.