Non-human identities such as AI agents, service accounts, API keys, and authentication tokens have become the most common initial access route into enterprise environments, according to new research from SpyCloud, which points to widening gaps between organizations’ confidence in their identity visibility and what they are actually monitoring.
The 2026 SpyCloud Identity Threat Report, released Sept. 9, is based on a survey of 750 cybersecurity leaders and practitioners at organizations with at least 500 employees across the United States, Canada, the United Kingdom and select European markets.
Among organizations that experienced identity-related security events, 31% identified compromised or overprivileged non-human identities, or NHIs, as their most common initial access vector. That was nearly twice the 17% that cited phishing and social engineering.
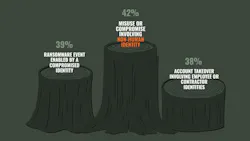
NHI-related misuse was also the most frequently reported type of identity-based event at 42%. Overall, 68% of organizations experienced an identity-based event during the previous year, with affected organizations averaging eight events.
The findings reflect an attack surface that is expanding well beyond traditional employee identities and endpoints, according to Trevor Hilligoss, SpyCloud chief intelligence officer and a former FBI and Department of Defense cyber investigator.
“The enterprise attack surface is no longer limited to employees and endpoints. It now extends across every AI agent, API key, token, service account, vendor and partner with access to business systems,” Hilligoss told SecurityInfoWatch.
As organizations expand their use of AI, automation and third-party services, those technologies are creating additional privileged connections that may fall outside established security governance and monitoring, Hilligoss added.
AI and non-human identity monitoring is lagging adoption
The report highlights a particularly large gap surrounding AI and machine identities. While 95% of organizations said they believe they have adequate visibility into AI- and NHI-related exposure, only 36% actually monitor those identities, making them the least-monitored identity risk category included in the research.
AI adoption is also moving faster than governance. SpyCloud found that 91% of organizations use AI tools or agents that can access internal systems, applications or data. Only 56%, however, have formal governance and ownership in place for AI- and NHI-related privileges. Another 41% rely on informal processes or partial ownership.
The report also identifies visibility gaps involving more established attack techniques. Organizations with visibility into stolen session cookies reported identity-based events at a lower rate than those without such visibility, 37% compared with 50%.
Phishing and malware remain significant components of identity attacks as well. Thirty-seven percent of respondents cited phishing and social engineering as common access paths, while 40% reported incomplete visibility into successful phishing events. According to the press release announcing the findings, 53% of organizations can identify malware exposure only on managed devices.
Third-party access is expanding enterprise identity risk
The expanding identity ecosystem also extends to suppliers, contractors and technology partners. Malware-infected third-party devices were cited by 23% of respondents as a leading cause of supply chain identity events, followed closely by exposed API keys or application access involving vendors and partners at 22%.
Nearly 40% of organizations lack a consistent process for confirming that a third-party identity exposure has actually been remediated. At the same time, 32% plan to increase investment in supply chain and vendor risk management during the next 12 to 18 months.
 Quiz